New VOLTA Infostealer uses Claude, Gemini and Kimi AI to classify victims by financial value

Cybersecurity researchers have discovered a new Windows infostealer malware called VOLTA-AUTODOXER (aka VOLTA) which uses a Large Language Model (LLM) to classify a victim’s stolen data based on its monetization value.
Like other typical thief families, VOLTA is equipped to harvest passwords and cookies from Chromium-based web browsers; data from Outlook profiles and Slack workspaces; payment cards; cryptocurrency wallet seed phrases; Discord, Telegram, Steam and Roblox sessions; Microsoft OAuth tokens; SSH and cloud provider keys; Wi-Fi profiles; and screenshots.
“VOLTA builds a set of structured evidence about the person behind the machine,” said Ryan Fetterman, a researcher at Cisco Talos. “This bundle contains geolocation and home address, employer and employer domain, inferred year of birth, last 4 digits of the card, Slack workspaces, document authorship metadata, iPhone save flags, and a live Roblox account rating.”
To make this information more valuable, the malware uses access to stolen sessions to search the victim’s Gmail account for receipts to corroborate the home address by extracting emails related to Amazon, DoorDash, Uber Eats, Grubhub, Walmart, and PayPal.
Once the necessary information is collected, everything is serialized and fed into an artificial intelligence (AI) system for analysis using OpenRouter, a unified LLM API gateway and routing service, as well as a system prompt. Requests are sent by default to Anthropic’s Claude Opus 4.6, otherwise they revert to Moonshot AI’s Kimi K2 and Google’s Gemini 2.5 Flash.
“VOLTA uses a multi-model architecture to resiliently fall back when a model is rejected, checking each response for phrases like “I can’t” or “I can’t,” before moving to a chain of up to three models,” Talos said.
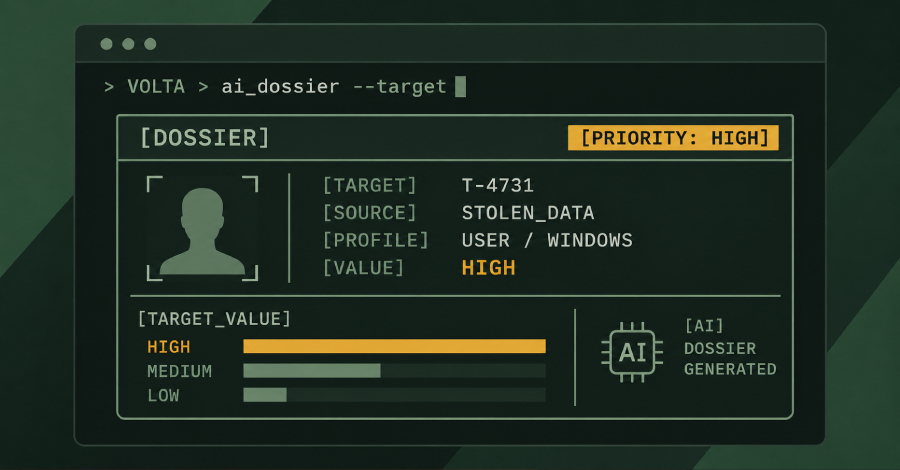
VOLTA provides a 240-word system prompt that asks the model to assume the role of a “forensic intelligence analyst” tasked with writing a target assessment based on data from a structured evidence set. “The bundle is the ONLY allowed source of facts; your training knowledge should never provide facts on the subject,” reads one line of the prompt.
“The required output includes a section titled ‘WHAT THEY’RE WORTH’ with valuables categorized by monetization with a low/medium/high level, and a section on ‘THEIR OPSEC’ containing an assessment of the victim’s security posture and password hygiene,” Talos explained.
“The model is the operator’s triage analyst; it transforms a raw credentials log into a prioritized, quote-supported case of the victim and their monetizable assets.”
Data exfiltration occurs via Telegram in three different stages:
- Right after the thief executes, containing details about browser passwords, cookies, payment cards, cryptocurrency wallets; Discord, Steam and Roblox tokens; Wi-Fi passwords and screenshots
- After the AI call, which includes captured data and LLM analysis results
- After the live enrichment stage, which includes Gmail receipts and order history
Additionally, VOLTA uses a model containing six slots filled at build time. This includes the Telegram channel used for data exfiltration, API keys, and other settings.
This approach suggests that the malware author is likely either promoting a build kit to potential customers or leveraging it as a bespoke tool under their control to compile a custom binary for each command.

“If VOLTA is indeed commoditized malware, then the AI file capability is not something the author invented for its own operations,” Talos said. “It’s a feature that allows a client of any sophistication level to point it at victims and start receiving categorized target ratings in their Telegram inbox.”
“VOLTA is a mature thief with a late-stage AI layer added for one purpose: to relieve the operator of analytical work. The focus for AI improvement here is not speed or scale but the displacement of effort.”
This disclosure comes as adversarial adoption of generative AI (aka GenAI) is quickly becoming the new normal, as malicious actors integrate the technology into their workflows to develop custom tools or find valuable data, increasing the chances of success of their attacks.
“GenAI technologies are also well-suited for examining massive amounts of data for content classification or search purposes,” Zscaler ThreatLabz said. “Once an attacker has access to the victim’s system, GenAI can therefore be used to search all documents that the victim’s system has access to, looking for the most valuable or sensitive data for theft or encryption in the next phase of the attack.”
A ransomware actor can leverage this method to identify and acquire the most sensitive data from a compromised network, maximizing the chance that the victim will pay.
Last week, Talos also detailed an AI-based framework called NIK C2 that provides attackers with remote access, credential theft, keylogging, defense evasion, surveillance, and ransomware capabilities, while integrating an OpenAI client to send the stolen data for AI analysis within the compromised session.
NIK C2, a Go-based Windows remote access tool, provides persistent control over compromised hosts and supports over 52 commands sent by a command and control (C2) server to collect a wide range of data.
The OpenAI integration is distinguished by the fact that the threat actor can abuse a victim’s own OpenAI API key to run the AI-based analysis. Concretely, the factory checks whether the actor has provided an API key. In the absence of such a string, it searches the victim’s environment variables for the string “OPENAI_API_KEY” and uses it.
This is a form of LLMjacking, in which malicious actors steal access to a third party’s AI model to conduct their own operations – in this case, against the victim themselves – while the rightful owner pays for the computing power. Additionally, it allows the attacker to evade detection by hiding the originator of the requests.
“This fallback is not a backup mechanism for API key resolution. It is a deliberate design with significant operational implications,” Talos said. “If the victim has set up an OpenAI account on their machine, the API key from that account will be used to fund the actor’s AI inference.”
“NIK C2 reshapes the adversary’s craft by consolidating collection and exploitation into a single, continuous session, erasing offline processing delays that historically granted defenders critical detection windows,” Talos said.
Gn bussni