
A security researcher demonstrated a software-only partial jailbreak of the Switch 2, gaining access “to user space” which he said “allows us to run homebrew, reverse engineer and modify Switch 2 games, back up Switch save files, and access most Switch 2 peripherals via MMIO.”
The hack builds on the original Switch version of SmileBasic 4, the latest in a long line of programming environments and interpreters running on Nintendo hardware. The so-called “connected” hack also requires access to a macOS or Linux PC on the same network to run a node.js package which allows privileged access to the system.
Researcher Sammy Hajhamid writes that he used OpenAI’s Codex to attack SmileBasic’s language interpreter, using a custom harness that could send USB commands to the system and display the results via HDMI (as well as power cycling via a Bluetooth light switch toggle device). After “a substantial effort of approximately 2 weeks”, this exploit discovered a 32-bit integer overflow that occurs when removing elements from an array in SmileBasic. This error provides access to an array pointer, which in turn allows read and write access to parts of system memory.
From there, Hajhamid writes that he began digging around for access to the Switch 2’s internal system modules, looking for ones that could provide more privileged access to the console’s core functions. Eventually, he found a buffer overflow in the console’s FileSystem services module that exposed a cached data pointer, granting arbitrary read and write privileges. From there, Hajhamid writes that it could perform “filesystem privileged actions” and possibly achieve native code execution through a fake filesystem process.
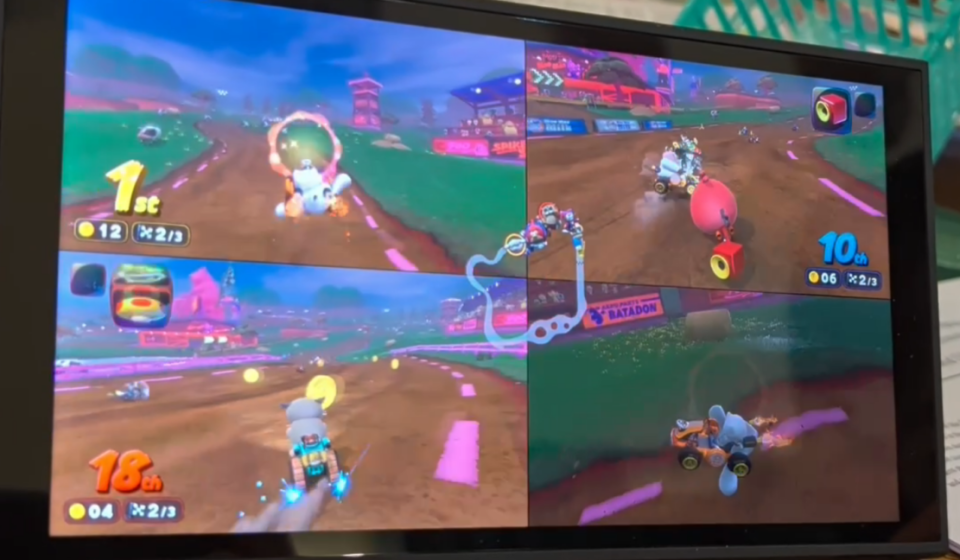
Hajhamid, who goes by Pepsipu online, introduced a host of new modified characters in Mario Kart World as proof of concept for the exploit. Others similarly demonstrate simple demos and in-progress development tools running on exploited hardware.
Gn tech