Windows 11 Zero-Day “SignDrop” Exploit Turns Microsoft’s Own Security Patch Against Itself and Grants SYSTEM Privileges
A recently disclosed zero-day vulnerability in Windows, dubbed SignDrop, could allow attackers with standard user privileges to gain full SYSTEM access by exploiting a security mechanism introduced by Microsoft last year. Ironically, the affected component was specifically designed to prevent similar privilege escalation attacks.
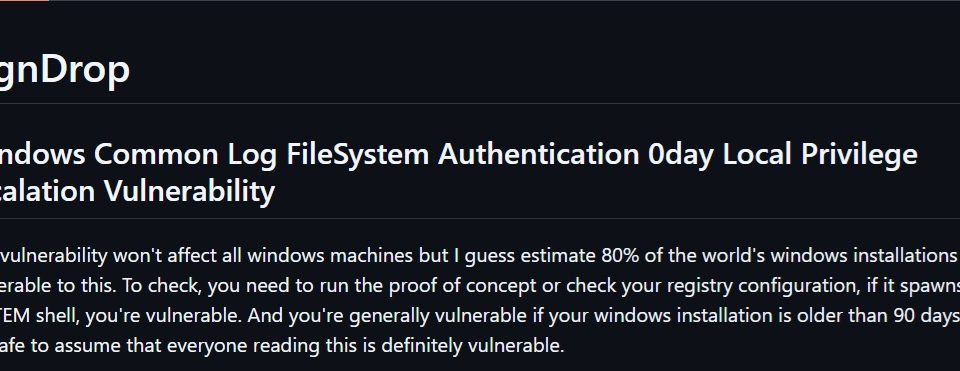
Security researcher Abdelhamid Nacerialso known as Nightmare Eclipse Or MSNightmarepublished on SignDrop Proof of Concept (PoC) on GitHub on November 10, 2026. The exploit targets Microsoft Common Log File System (CLFS) driver, which manages logging operations for Windows applications and system services.

SignDrop leverages Windows Defender and CLFS to gain SYSTEM privileges
Microsoft presented Strengthening CLFS authentication In October 2025 to address long-standing security vulnerabilities. Mitigation uses cryptographic authentication codes to verify the integrity of log files before the driver processes their contents.
However, Naceri discovered that the authentication mechanism itself can be manipulated to create files with elevated privileges.
Specifically, vulnerability affects how the clfs.sys the driver creates a companion .cnpf authentication files. An attacker can prepare a specially crafted log file and then force a privileged Windows process, such as Microsoft Defender, to open it..
 “.” class=”wp-image-1756668″ srcset=”https://cdn.wccftech.com/wp-content/uploads/2026/11/Terminal.jpg 1634w, https://cdn.wccftech.com/wp-content/uploads/2026/11/Terminal-564×254.jpg 564w, https://cdn.wccftech.com/wp-content/uploads/2026/11/Terminal-728×328.jpg 728w, https://cdn.wccftech.com/wp-content/uploads/2026/11/Terminal-767×346.jpg 767w, https://cdn.wccftech.com/wp-content/uploads/2026/11/Terminal-1536×693.jpg 1536w, https://cdn.wccftech.com/wp-content/uploads/2026/11/Terminal-1456×657.jpg 1456w” sizes=”auto, (max width: 1634px) 100vw, 1634px”/>
NT AUTHORITY\SYSTEMgenerating a SYSTEM level command prompt, as confirmed by the whoami order. Image credit: SignDrop proof-of-concept GitHub repository.Through this interaction, CLFS can create an authentication file using SYSTEM privileges while retaining the access permissions inherited from the file controlled by the attacker. Combined with additional manipulations, this allows an ordinary user to elevate their privileges.
The researcher also states that the technique could bypass antivirus and endpoint detection and response (EDR) tamper protectionsince privileged file operations appear to originate from legitimate security processes.
Independent cybersecurity researchers at Cyderes successfully reproduced the exploit and got a SYSTEM level command shellconfirming that the technique works under certain conditions.

Microsoft investigates SignDrop as researchers warn of widespread exposure
Naceri tested SignDrop against Windows 11 26H2, Windows 11 26H2 experimental, and Windows Server 2025 experimentalestimating that approximately 80% of Windows installations could be vulnerable. However, this figure remains unverified and independent researchers have reported compatibility and reliability limitations.
Users can inspect the following location in the Windows registry to determine whether the affected CLFS authentication mechanism is enabled:

HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\CLFS\Authentication\Mode

Mode = 1)one of the configurations potentially vulnerable to the SignDrop zero-day exploit. Image credit: Wccftech.According to Microsoft documentation, a value of 0 (application mode) Or 1 (learning mode) indicates active mitigation and potentially vulnerable configuration. However, this alone does not guarantee that the exploit will succeed.
It is important that users do not disable CLFS authentication as a workaround, because this could expose their computers to old memory corruption vulnerabilities.
Microsoft is aware of the reports and is investigating the vulnerability. In a statement provided to Safety Weekthe company said Microsoft Defender can detect and block exploitation attempts, adding that it has not found any evidence of active exploitation in the wild..
At the time of writing, SignDrop has not received an official CVE designation or dedicated security patch. Users should continue to install Windows and Defender security updates while awaiting further guidance from Microsoft.
Information source: SignDrop proof of concept GitHub repository

About the author: Sebastian Castellanos is a data scientist by education and training. He is also deeply passionate about PC gaming hardware and software. He recently started writing technical articles and guides on Wccftech about PC hardware, gaming and mods.
Follow Wccftech on Google to get more of our news coverage in your feeds.
Gn tech